At a glance
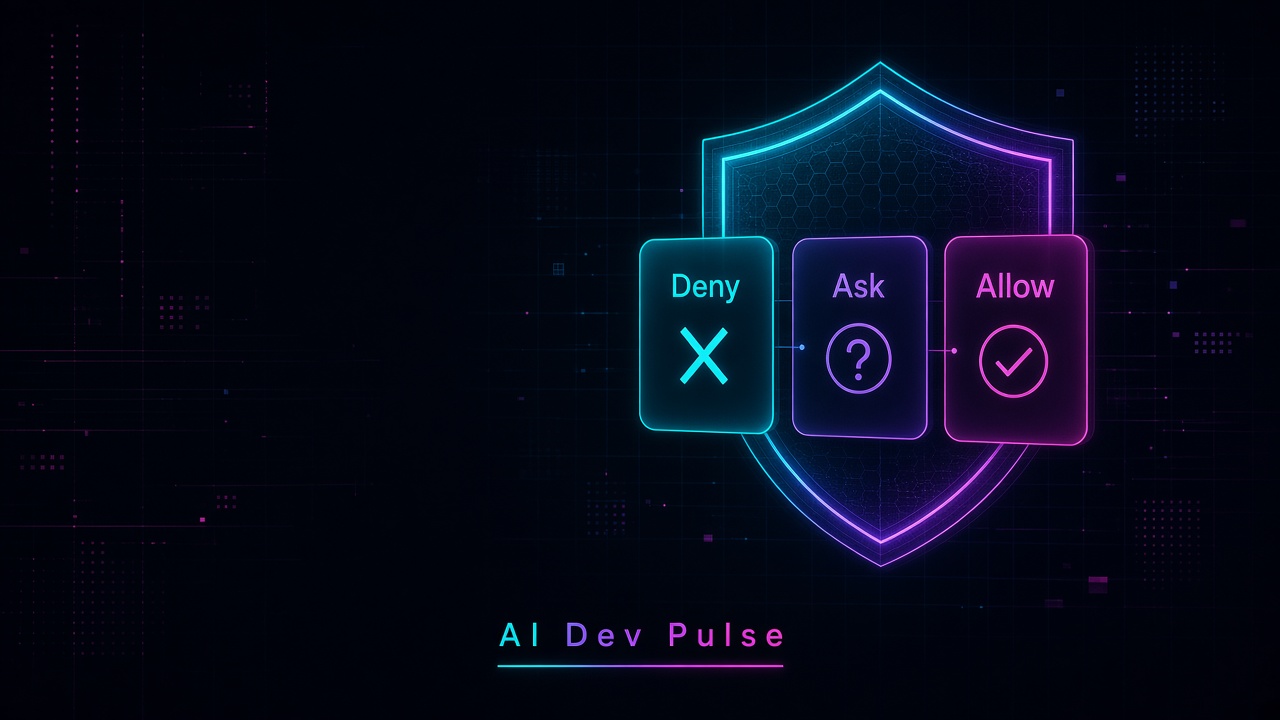
- GitHub Copilot can now pin enterprise deny/ask/allow rules for agent shell, file, and network operations.
- Code Quality agentic autofix lets you Assign to Copilot up to 25 backlog findings in one shot.
- Claude Code v2.1.267 adds `maxEffortLevel`, a prompt-snapshot toggle, and a large prompt-cache and resume fix pack.
- Gemini CLI v0.59.0 blocks SSRF in MCP OAuth discovery and fail-closes workspace trust for `mcpServers` in restricted mode.
September 10 is a Thursday control-plane and remediation day, so the useful work is how these four moves fit together. Org policy can pin what Copilot agents may run without a prompt, Code Quality debt can move in bulk to an agent PR, Claude Code can cap provider effort and keep caches warm across resumes, and Gemini CLI hardens MCP auth paths.
Treat today as a permissions-and-backlog day. Draft a `managed-settings.json` deny/ask/allow matrix for Copilot agent ops, try a 10 to 25 finding Assign to Copilot batch on a Code Quality-enabled repo, pin Claude Code to v2.1.267 with an effort ceiling, and upgrade Gemini CLI before you widen MCP OAuth servers.
Top Stories
GitHub Copilot enterprise managed permissions for agent operations
Practical dev impact: Shell, filesystem, and network approvals are no longer a per-developer habit, because Business and Enterprise admins can now set centrally which agent operations are blocked, need a fresh human approval, or may proceed without a prompt. GitHub’s September 9 changelog marks the controls generally available in the Copilot app, Copilot CLI, and Visual Studio Code sessions that use Agent Host. Managed restrictions cannot be weakened by user or workspace settings, auto-approval, or previously saved approvals, and you can specialize policies per enterprise team. The managed-settings reference documents `permissions.deny`, `permissions.ask`, and `permissions.allow` with `Shell(…)`, `Read(…)`, `Edit(…)`, and `Domain(…)` selectors, plus deny > ask > allow precedence. Pair this with yesterday’s JetBrains managed sandbox story if your fleet spans IDEs.
Code Quality agentic autofix can burn down up to 25 findings per assign
Practical dev impact: On the Code Quality backlog page, you can select up to 25 standard findings and Assign to Copilot in one action so the agent fixes them on a branch, validates its own changes, then opens a pull request for review. GitHub shipped this September 9. Assign to Copilot replaces Generate fix for individual findings, so one flow covers a single finding or a batch. There is no separate policy toggle: if the enterprise already allows GitHub Code Quality, bulk remediation is included, and assigning findings consumes AI credits. Availability is repositories with GitHub Code Quality on GitHub Team and GitHub Enterprise Cloud (including data residency). Keep human review on the opened PR, especially when the batch spans security-sensitive paths.
Claude Code v2.1.267: maxEffortLevel, prompt snapshot toggle, cache fixes
Practical dev impact: Pin `@anthropic-ai/claude-code@2.1.267` so admins can set `maxEffortLevel` (top-level or per model under `modelSettings`) to cap effort on Bedrock, Vertex, and Foundry while still allowing lower user choices, and use `–system-prompt-snapshot off` when you are iterating on system prompt text and need a fresh render each request. npm published v2.1.267 on September 9 (about 18:25 UTC), and the GitHub release landed the same day (about 19:58 UTC). The drop also fixes marketplace path containment with backslashes, fail-closed behavior when managed hook URL lists are unreadable, large-session resume dropping parallel tool calls over 5 MB transcripts, and a long list of prompt-cache breaks around MCP reconnects, `/model` switches, and `-p` resume into interactive mode. Prefer an explicit version pin over `latest` or `stable` drift (`stable` still trailed at v2.1.236 when checked).
Gemini CLI v0.59.0 hardens MCP OAuth and restricted-mode trust
Practical dev impact: Upgrade `@google/gemini-cli` to `0.59.0` before you point agents at new MCP OAuth servers or run in restricted workspace trust, because the release prevents SSRF in MCP OAuth metadata discovery and authentication and enforces fail-closed workspace trust while filtering `mcpServers` in restricted mode. GitHub published the tag September 8 (about 21:13 UTC), and npm recorded the same version minutes later. Treat this as a security patch for terminal agent fleets that still run Gemini CLI (including enterprise Code Assist paths), not a feature drop. Re-test MCP OAuth connect flows and confirm restricted-mode sessions no longer inherit untrusted MCP server configs after upgrade.
Practical Impact Analysis
Today’s through-line is who owns agent runtime permissions, and how fast you can spend AI credits to clear quality debt. Copilot’s managed deny/ask/allow rules close the gap between agents being useful and agents being able to `rm`, edit `/etc`, or hit unapproved domains. If you already ship `managed-settings.json` for models, plugins, or YOLO disablement, agent operation selectors are the next commit, not a new product project.
Code Quality bulk autofix is the spend side of the same coin. Twenty-five findings in one Assign to Copilot action can clear a sprint of nits, but it also burns credits and opens a PR that still needs review. Start with a non-blocking severity band or a single service directory so you learn the agent’s validation behavior before you point it at auth or payments code.
Claude Code v2.1.267 is mostly operational hygiene after yesterday’s v2.1.265 and v2.1.266 wave. `maxEffortLevel` matters for Bedrock, Vertex, and Foundry fleets that cannot afford unbounded high-effort loops, while the prompt-cache and resume fixes matter for anyone running long `-p` jobs or MCP-heavy sessions. Pin the version in images and Actions the same way you pin language runtimes.
Gemini CLI v0.59.0 is the reminder that MCP OAuth metadata endpoints are part of your attack surface. Fail-closed restricted mode is the right default when a workspace is not fully trusted, so upgrade the CLI before you expand the MCP allowlist.
If you only do three things this morning, commit a starter Copilot `permissions.deny`/`ask`/`allow` matrix, run one bounded Assign to Copilot Code Quality batch, and bump Claude Code pins to v2.1.267 (plus Gemini CLI to v0.59.0 on machines that still use it).
Tutorial
Ship a starter Copilot managed permissions matrix for agent shell, files, and domains. Use this when Business or Enterprise admins already host `copilot/managed-settings.json` in the enterprise `.github-private` repo, or deploy the same JSON via MDM or file-based paths.
1. Start from the deny/ask/allow example below and tune selectors to your risky paths and domains.
2. Commit the JSON under `copilot/managed-settings.json` on the default branch of the source org’s `.github-private` repository, or merge it into your existing file.
3. Restart Copilot CLI or VS Code Agent Host sessions, or wait for the hourly refresh.
4. Verify a denied shell is blocked and an `ask` rule still prompts even after a prior approval. Tighten team overrides only after the enterprise default is boring and enforceable.
Recommended AI prompt
Copy this paragraph into ChatGPT, Claude, Gemini, Grok, or whatever you use.
You are my staff engineer for coding-agent permissions and remediation on 2026-09-10. GitHub Copilot now ships enterprise-managed deny/ask/allow rules for agent shell, file, and network operations in the Copilot app, CLI, and VS Code Agent Host, and those rules cannot be weakened by user settings or saved approvals. Code Quality agentic autofix lets you Assign to Copilot up to 25 findings so Copilot opens a validated PR, and that flow consumes AI credits under existing Code Quality policy. Claude Code v2.1.267 adds `maxEffortLevel`, `–system-prompt-snapshot off`, and a large prompt-cache and resume fix pack. Gemini CLI v0.59.0 hardens MCP OAuth against SSRF and fail-closes restricted-mode `mcpServers`. Ask which Copilot clients, Code Quality repos, Claude Code pins, and Gemini CLI hosts we run. Then produce a deny/ask/allow matrix for our risky paths and domains, a first Assign to Copilot batch plan with credit and review gates, a v2.1.267 pin plus `maxEffortLevel` rollout, and a Gemini CLI v0.59.0 upgrade checklist for MCP OAuth. Keep it concrete and copy-paste ready.