At a glance
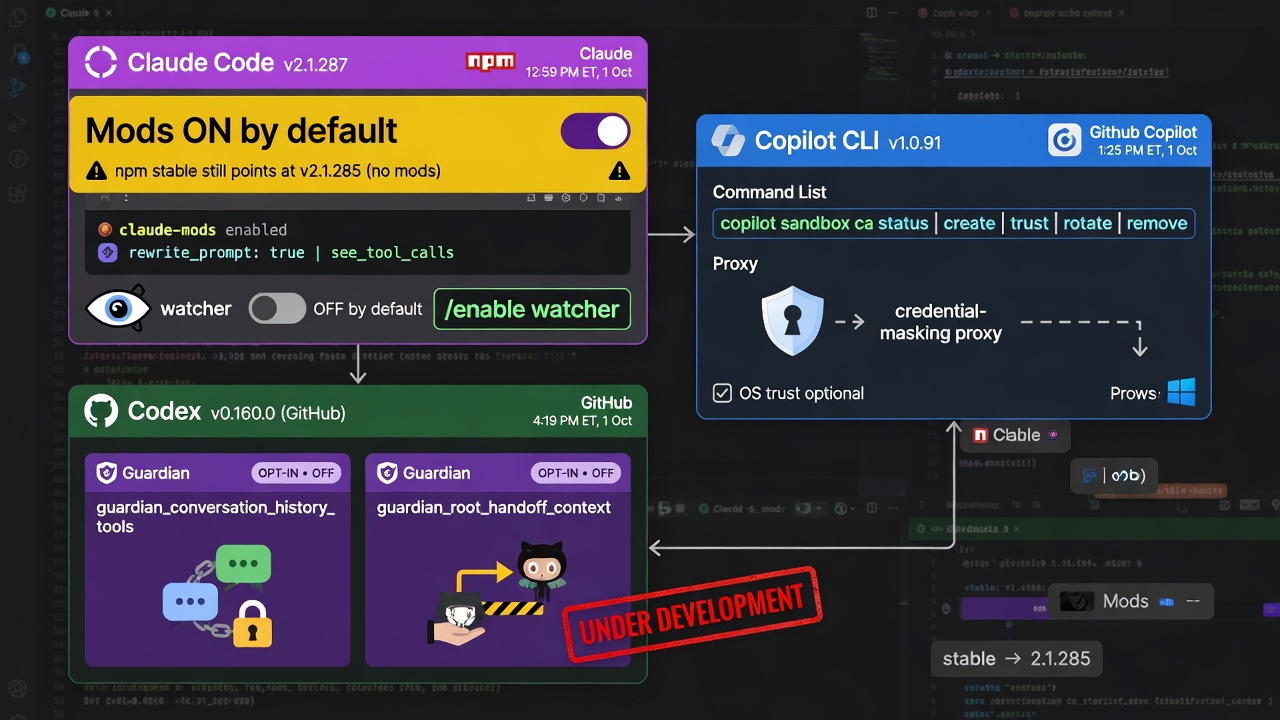
- Claude Code v2.1.287 (npm, 12:59 PM ET, 1 Oct) turns Claude Mods on by default, so a plugin can run code that sees and rewrites prompts and tool calls, but npm's
stabletag still points at v2.1.285, which has no mods. - Its built-in "You should know" side agent, which this brief calls the watcher, is off by default and takes one command to enable.
- Copilot CLI v1.0.91 (1:25 PM ET, 1 Oct) adds
copilot sandbox ca status|create|trust|rotate|removefor the certificate authority behind the sandbox's credential-masking proxy, and operating-system trust is optional. - Codex v0.160.0 (GitHub, 4:19 PM ET, 1 Oct) adds two opt-in Guardian features,
guardian_conversation_history_toolsandguardian_root_handoff_context, both under development and off.
Today’s three changes decide what may see or rewrite a session, and only one arrives switched on. Claude Code mods are on for anyone who updates to v2.1.287, so an administrator has to decide who may install them, while the watcher, Codex’s Guardian history and Copilot’s operating-system certificate trust stay off until someone opts in.
Treat today as the day you decide who may run code inside Claude Code, leave the watcher and Guardian history off until a reviewer has read what they send, and run copilot sandbox ca status before trusting a certificate.
Top Stories
1. Claude Code v2.1.287 makes mods a default surface
A mod is a plugin whose JavaScript or TypeScript handlers run inside Claude Code, so unlike a settings hook, which runs a command outside the process, it can rewrite or answer prompts, tool calls and turns, and it can approve or deny a tool call before the permission prompt appears. Anthropic’s docs say mods are on by default from v2.1.287, are not sandboxed, and run with the installing user’s permissions. Their hooks also run in the VS Code panel, claude -p and the Agent SDK, but only the terminal and Desktop draw anything.
Administrators get one switch for user-installed mods. In managed settings, set allowManagedModsOnly on the built-in guard under pluginConfigs, keyed cc-plugin-sec-default@builtin. It blocks mods a user installs, loads with --plugin-dir or has Claude write, and it leaves settings hooks and built-in mods running. The guard itself loads only on machines with managed settings or for Team and Enterprise sign-ins, so an API-key user on an unmanaged laptop has none, and where it does load, a deny rule still beats a user’s mod.
Some Claude Code features are now built-in mods, and disableAllHooks, --bare and --safe-mode do not stop them. One is cc-plugin-you-should-know, a side agent that watches longer tasks and shows a note above the prompt. It is off by default and listed under /plugin, Installed, Show disabled, when your organization has it. The changelog says to enable it with /plugin enable cc-plugin-you-should-know@builtin for first-party sessions with telemetry on, a phrase it does not define, and neither it nor the docs say what the agent sends or which model it uses. In an isolated test, claude plugin enable and claude plugin disable with that id wrote the enabledPlugins entry from a shell, though we did not run the side agent itself.
Two config changes ride along: MCP servers on the 2025-11-25 protocol can now send URL prompts, so one that stops connecting needs "bareElicitationCapability": true on its config entry, and the OpenTelemetry user_prompt event gains prompt_text, a copy of prompt to be masked wherever prompt is.
Practical dev impact: If your fleet follows npm’s stable tag, which pointed at v2.1.285 at 6:01 AM ET today, it does not have mods yet, so the time to set allowManagedModsOnly is before that tag moves, and we did not check the native installer’s stable pointer. Keep the watcher off in shared images, because what it sends is undocumented. Prompt text is redacted unless OTEL_LOG_USER_PROMPTS=1, so prompt_text matters only for teams that log prompts.
2. Copilot CLI v1.0.91 turns the sandbox proxy certificate into a command
Copilot CLI v1.0.91 shipped at 1:25 PM ET on 1 Oct. Its changelog says copilot sandbox ca checks, creates, trusts, rotates and removes proxy CA trust, and that /sandbox ca install becomes create and trust. In the shipped build the verbs are status, create, trust, rotate and remove, and check and install are rejected as unknown subcommands.
The authority belongs to the credential-masking proxy that sandboxed git, gh and masked environment variables use, not to a corporate inspection proxy. Sandboxed commands already receive a certificate bundle through environment variables such as SSL_CERT_FILE, so operating-system trust is only a compatibility fallback for clients that ignore them. The authority is unique to each Copilot home and limited to GitHub hosts plus your saved credential hosts.
By the help text, trust differs by platform. On macOS trust writes the login Keychain and asks for your password, on Windows it writes the machine root store after administrator approval, and Linux uses the per-process bundle only. status exits 0 when trusted, 3 when not, 4 when the platform has no operating-system trust, and 5 when a rotation is needed. Sandboxing is experimental and off by default, and the help says /sandbox appears only with --experimental or a managed policy. The build also offers a Windows network bypass for Node and npm EACCES socket denials, and an approved bypass skips masking and the proxy, so the command may see real credentials.
Practical dev impact: Run status first and leave operating-system trust off unless a named client fails. Windows trust is machine-wide, and the private key is readable by any program you run, so protect the Copilot home like a password. Decline bypass offers unless the command cannot run any other way. We ran the commands only on Linux, where create and trust fail as unsupported, so the macOS and Windows details come from the help text.
3. Codex v0.160.0 adds two Guardian features that stay off
Codex v0.160.0 reached GitHub at 4:19 PM ET on 1 Oct. Its release note says it adds opt-in Guardian review capabilities to retrieve earlier user instructions and include context from agent handoffs, which is two features, not one. guardian_conversation_history_tools lets the reviewer search and read earlier user messages, because the transcript it normally sees may omit earlier instructions, restrictions or revoked permissions. With Apps enabled it rechecks the parent’s tool policy on each call. guardian_root_handoff_context selects worker-specific context around recorded agent handoffs. Both show as “under development” and false in codex features list.
Guardian, called Auto-review in the docs, is Codex’s reviewer agent. It runs only when approvals_reviewer = "auto_review" (the default is user) and approvals are interactive, and it changes who reviews an approval without granting permission. To opt in, use codex --enable guardian_conversation_history_tools, -c features.guardian_conversation_history_tools=true, or codex features enable guardian_conversation_history_tools, which writes [features] in config.toml. The release also stops queued messages sending twice after a reconnect and keeps server provider, reasoning-summary and verbosity settings in the terminal UI and fixes which sessions show in resume and fork history.
Practical dev impact: Take the upgrade for the resume and queue fixes, which rest on the release note, and leave both Guardian flags off in fleet config. Try them only in a scratch profile, because both are under development and could change.
Practical Impact Analysis
Today’s controls are asymmetric. Claude Code mods ship enabled, so the work is to decide who may install them before your channel reaches v2.1.287, while the watcher, Guardian history and operating-system proxy trust all start off and should stay off until there is a named reason. That means allowManagedModsOnly in managed settings for Claude Code, status as the one Copilot command safe to run everywhere, and a scratch profile for the under-development Guardian flags.
Tutorial
Step 4 is by hand, and the script covers the rest.
- Check the client versions and which Claude Code tag your channel follows.
- Write the managed-settings snippet from Anthropic’s docs that blocks user-installed mods. The script only writes an example file, so deploy it through your own managed-settings channel.
- Keep the watcher off, and set
MOD_DIRto an unfamiliar mod to see itshooks:andcalls:lines. - If you log prompts with
OTEL_LOG_USER_PROMPTS=1, addprompt_textto the same drop or mask rule asprompt. - Check the Copilot sandbox certificate with
statusbefore trusting it. - Confirm both Guardian flags read
false.
You are done when the versions print, claude plugin disable reports success, status prints one of the exit codes above (4 on Linux), and both Guardian lines end in false. We did not deploy the snippet to a managed machine, so review the example file before you do.
Recommended AI prompt
Copy this paragraph into ChatGPT, Claude, Gemini, Grok, or whatever AI you use.
I run a small engineering team that uses Claude Code, Copilot CLI and Codex. Claude Code v2.1.287 turns mods on by default, has an allowManagedModsOnly setting that works only in managed settings under cc-plugin-sec-default@builtin, and ships an off-by-default “You should know” side agent, Copilot CLI v1.0.91 adds copilot sandbox ca subcommands for its credential-masking proxy certificate, and Codex v0.160.0 adds two under-development Guardian features that are off by default. Write a one-page checklist that says, in order, what to verify on one developer laptop, what to put in managed settings, and what to leave off, naming the exact command or setting and the risk it avoids for each item. Do not tell me to enable the side agent or the Guardian features, do not invent flags, settings or versions I did not give you, and ask me for anything you need, such as our operating systems or whether prompt logging is on, instead of guessing.
Sources
- Claude Code v2.1.287 release
- Claude Code CHANGELOG
- Claude Code docs changelog
- Claude Code mods overview
- Claude Code mods admin guide
- Claude Code monitoring docs
- Claude Code issue 70763
- Copilot CLI v1.0.91 release
- Copilot CLI changelog
- Codex v0.160.0 release
- Codex changelog
- Codex Auto-review docs
- Codex config reference
Recommended AI prompt
Explore each Top Story in Grok. Links open in a new tab. On phones, the same link may open the Grok app if you have it installed (via your device's normal link handling).
Article: Claude Code Mods Ship On by Default While Copilot and Codex Stay Opt-In
Privacy: links open grok.com in your session only. AIDevPulse does not run your prompts through our API.